Request intake
Open a case with the request type, subject reference, dates, scope and responsible owner.
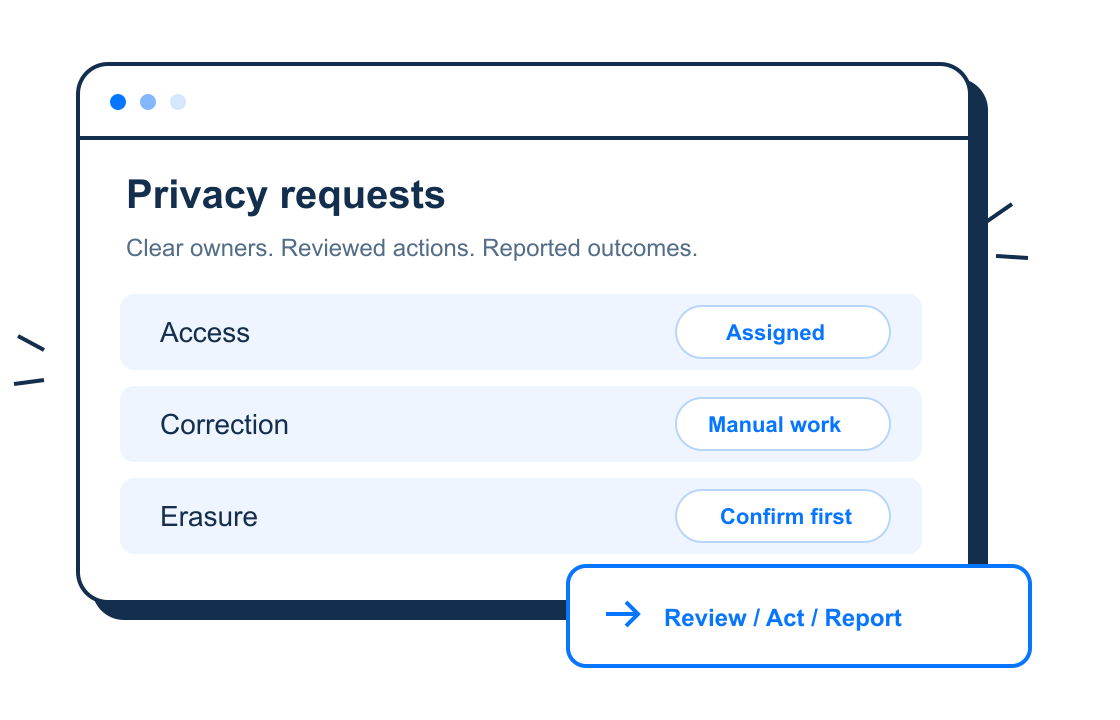
Support DPDP and GDPR privacy-rights operations by coordinating access, correction and erasure requests across people, systems and processors, with clear ownership and an audit trail.
Start with one workflow, connect the systems in scope, and expand only after the control has been tested.
Open a case with the request type, subject reference, dates, scope and responsible owner.
Record the checks and approvals required before protected information is returned or changed.
Track work assigned to internal systems, service owners and external processors.
Preserve status, decisions, exceptions and completion evidence without placing sensitive values in receipts.
Capture the request and apply the organization’s identity and authorization process.
Coordinate the approved access, correction or erasure work across configured systems.
Record the response, exceptions, completion state and supporting evidence.
Securelay coordinates configured workflows and protected records. Your organization remains responsible for identity standards, legal exceptions, response content, deadlines and systems that have not been integrated.
Explore the primary sources and practical implementation decisions in our field notes.