Notices and independent choices
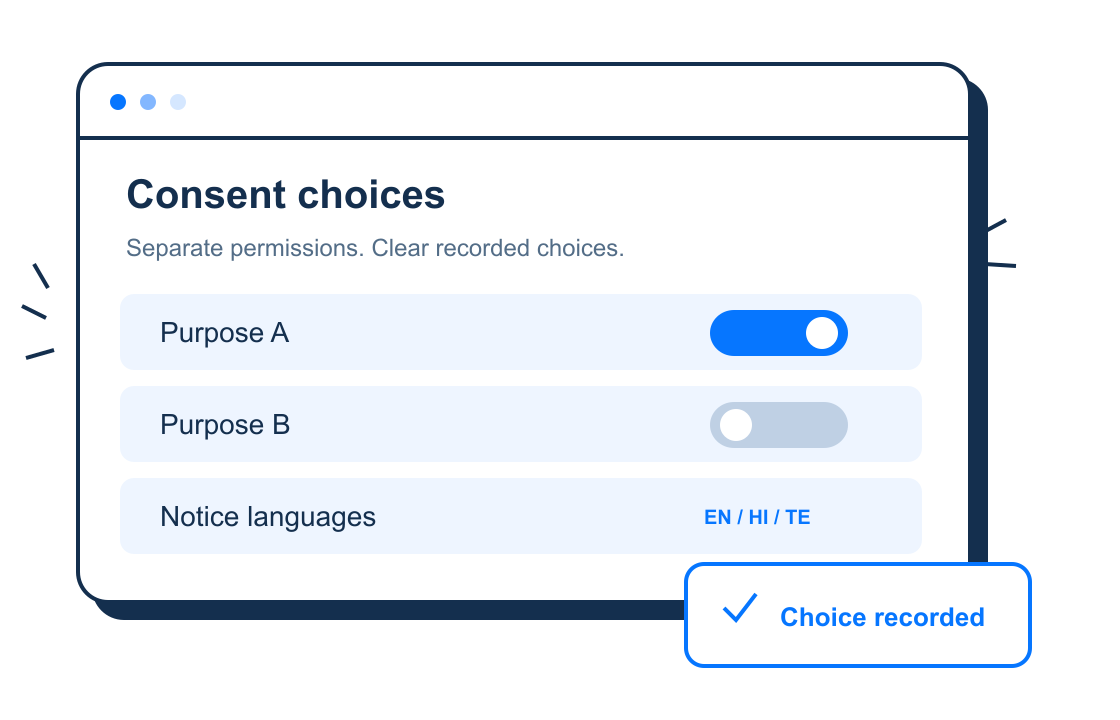
Define purposes and fields, publish notice versions in configured languages, and keep optional choices separate.
Create and publish notices, collect purpose-specific choices through your own application, and follow withdrawals through to reported client completion.
Start with one workflow, connect the systems in scope, and expand only after the control has been tested.
Define purposes and fields, publish notice versions in configured languages, and keep optional choices separate.
Record the client’s stable User ID, supplied email, the notice shown and each recorded choice. Cookie visitors can stay anonymous.
Single and batch checks return the current decision. A withdrawal denies the selected purpose; client pipelines must enforce that decision.
Send signed stop-processing work through a tested connection, or record manual outcomes. Delivery and reported completion stay separate.
Configure the notice, choices and languages. Your client application displays it in its own branding.
Your authenticated backend sends the person’s choice and checks the relevant permission before processing.
Deny the selected permission, request stop-processing work and track the result reported by the client or staff.
Client software enforces consent in its own jobs and APIs. Correction requests stay manual; client-reported completion is not independent proof. Legal basis, notice wording and validity remain decisions for your organization and qualified advisers.
Explore the primary sources and practical implementation decisions in our field notes.